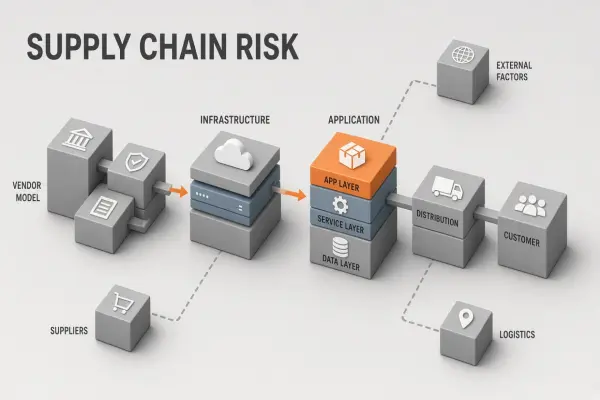
AI Supply Chain Risk: Vendors, Subprocessors, and Model Provenance
Manage AI supply chain risk across model providers, hosting regions, fine-tuning partners, and embedded AI features in SaaS you already buy.
Insights, guides, and latest trends from the world of AI tools
Manage AI supply chain risk across model providers, hosting regions, fine-tuning partners, and embedded AI features in SaaS you already buy.
Govern synthetic data used with AI tools: generation methods, re-identification risk, labeling, retention, and when synthetic data still triggers privacy review.
Detect shadow AI with network signals, expense audits, SSO gaps, and employee surveys, then route discoveries into your AI inventory without punishing reporters.
Navigate conformity assessment paths for high-risk AI tools: internal control, notified body involvement, technical documentation, and post-market monitoring.
Evaluate vendor model cards before procurement: required fields, limitation claims, bias disclosures, and when model cards are insufficient for due diligence.
Run algorithmic impact assessments before deploying AI tools: stakeholder mapping, harm scenarios, mitigation controls, and sign-off documentation.
Design a red teaming program for AI tools: attack surfaces, test cadence, severity scoring, remediation SLAs, and audit evidence regulators expect.
Write a foundation model usage policy covering approved models, data classes, fine-tuning rules, GPAI provider obligations, and exception workflows.
Standard labels when work products used AI assistance—internal and external consistency.
Didn't find tool you were looking for?