Model Card Review Process for Third-Party AI Tools
Evaluate vendor model cards before procurement: required fields, limitation claims, bias disclosures, and when model cards are insufficient for due diligence.
Insights, guides, and latest trends from the world of AI tools
Evaluate vendor model cards before procurement: required fields, limitation claims, bias disclosures, and when model cards are insufficient for due diligence.
Run algorithmic impact assessments before deploying AI tools: stakeholder mapping, harm scenarios, mitigation controls, and sign-off documentation.
Design a red teaming program for AI tools: attack surfaces, test cadence, severity scoring, remediation SLAs, and audit evidence regulators expect.
Write a foundation model usage policy covering approved models, data classes, fine-tuning rules, GPAI provider obligations, and exception workflows.
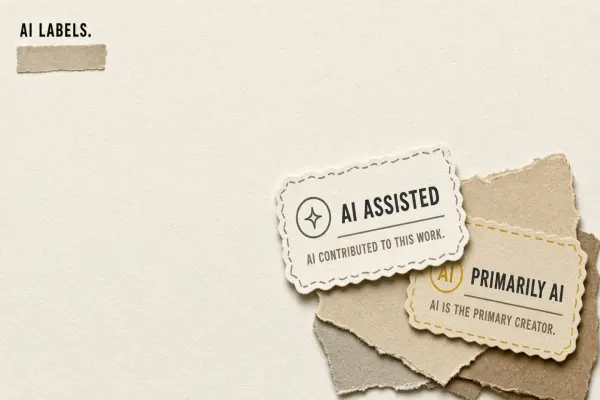
Standard labels when work products used AI assistance—internal and external consistency.
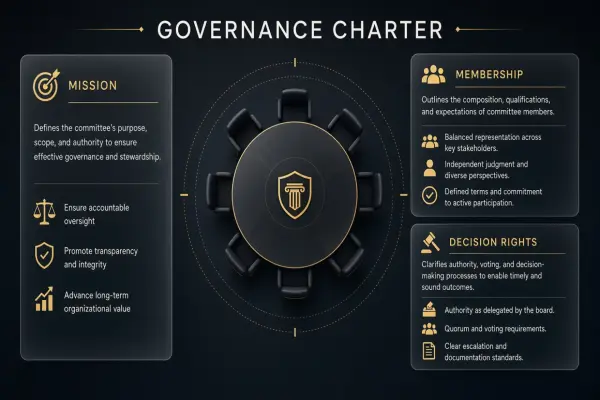
Charter template defining mission, membership, decision rights, and meeting cadence.
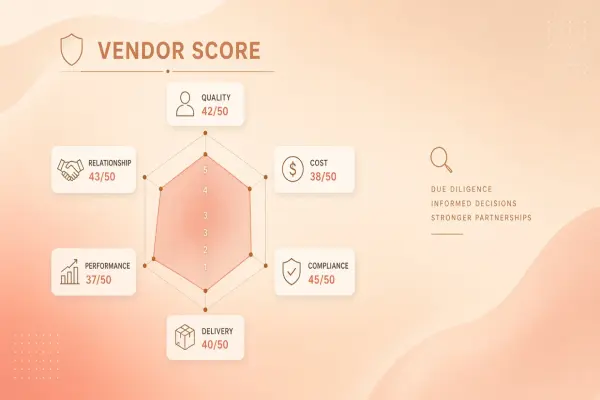
Scorecard weighting security, privacy, model transparency, and business continuity for AI vendors.
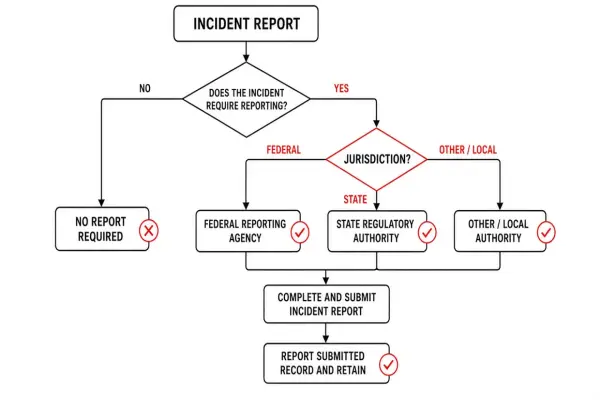
Framework for deciding when AI incidents require regulator notification beyond breach laws.
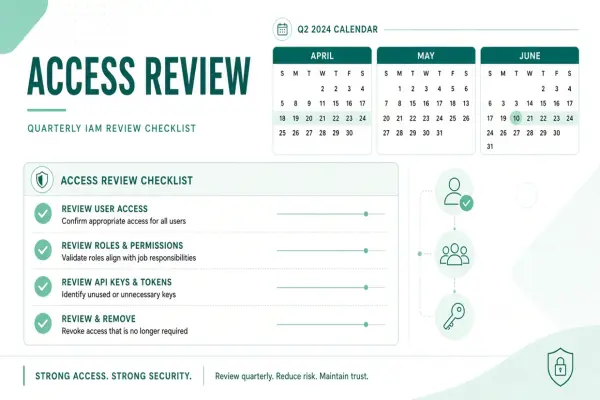
Quarterly access reviews for AI tools catch orphaned accounts and privilege creep.
Didn't find tool you were looking for?