Marketing teams want AI to draft emails, landing page copy, and campaign briefs inside HubSpot where contacts and attribution already live. Without integration architecture, models overwrite GDPR consent fields, send non-compliant email drafts, and break UTM consistency across channels.
Integrating AI tools with HubSpot Marketing Hub requires private apps with scoped OAuth, explicit contact property write policies, compliance checkpoints before publish on AI email drafts, and UTM consistency across generated assets. This guide covers marketing operations and platform owners connecting AI automation pipelines and AI research workflows to HubSpot CRM objects. The goal is faster content production without compliance or attribution regressions.
Integration Goals and Marketing Threat Model
Define which HubSpot objects, properties, and publishing actions the AI integration may touch before creating private app credentials. Common goals include email draft generation, blog outline creation, contact enrichment narratives, and campaign performance summaries. Threats include writing to lawful basis fields, generating CAN-SPAM violations, and inventing UTM values that fragment analytics.
- Scope: Marketing Hub emails versus Sales Hub deal properties.
- Retention: vendor storage of contact snippets and email bodies.
- Identity: mapping HubSpot user IDs for draft authorship audit.
- Publishing: draft-only versus scheduled send permissions.
Private App Scopes and Webhooks
Create HubSpot private apps with the minimum OAuth scopes for CRM read, marketing email draft write, and webhook subscriptions you actually use; rotate tokens when agencies or vendors offboard. Private apps replaced legacy API keys for new integrations. Scopes are granular: crm.objects.contacts.read is separate from content.write and automation actions.
- Register the private app in HubSpot Settings with a name tied to the AI vendor or internal service.
- Request read scopes for contacts, companies, and campaigns needed for personalization context.
- Request write scopes only for draft objects and custom AI properties, not subscription status fields.
- Subscribe webhooks to contact.propertyChange and marketing email events for sync, not the entire CRM firehose.
- Store access tokens in a secrets manager; refresh before expiry using the documented token endpoint.
| Scope area | Typical AI use | Avoid |
|---|---|---|
| crm.objects.contacts.read | Personalize email intros from job title and industry | Bulk export of entire contact database to external training |
| content.write | Create email and landing page drafts | Publishing without human compliance review |
| automation | Enroll contacts in workflows after AI qualification | Unreviewed enrollment rules that spam cold lists |
| webhooks | Trigger re-personalization when properties change | Subscribing to all object types without filters |
Webhook Signature Verification
Verify HubSpot webhook v3 signatures on every inbound request before enqueueing AI personalization jobs. Forged contact update events could trigger expensive model calls or leak data across tenant boundaries in multi-tenant middleware. Reject stale timestamps outside your replay window.
Contact Property Write Policies
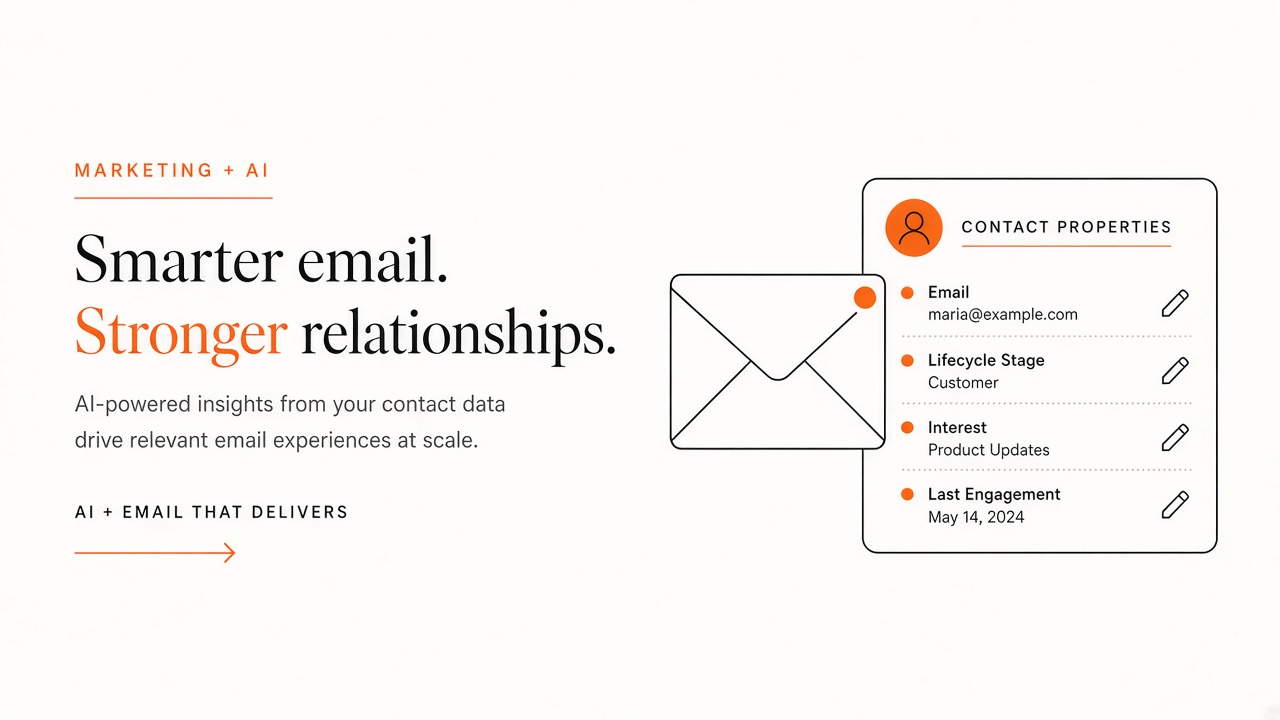
AI integrations must not write to GDPR lawful basis, email opt-out, or subscription type properties; limit writes to custom AI draft fields and enrichment fields marketing ops approves. A model that sets hs_email_optout to false would violate consent regulations. Treat consent and subscription fields as read-only for all AI service accounts.
- Maintain an allowlist spreadsheet: property internal name, direction (read/write), owner team.
- Custom fields like ai_personalization_snippet for draft text reps promote manually.
- Block writes to lifecycle stage unless a named workflow explicitly delegates that automation.
- Log old and new values for every AI write with hubspot_owner_id attribution.
- Run weekly audits comparing AI-written properties to human corrections.
GDPR and Privacy Fields
Properties related to GDPR consent, data processing agreements, and regional privacy flags are never AI writable. Legal teams should sign off on the allowlist quarterly. European contacts may require additional checks before AI personalization uses their company name in email copy.
Email and Landing Page Draft Flows
Route AI-generated marketing emails and landing pages into HubSpot as drafts assigned to a human owner; run CAN-SPAM compliance checks before any send or schedule action. Required elements include accurate From identity, physical mailing address in footer, and functional unsubscribe link HubSpot injects on send, not the model.
- Generate subject line and body in external AI or HubSpot native tools; save as draft via API.
- Compliance checklist: physical address present, no deceptive subject lines, unsubscribe not removed.
- Brand review: tone guide, prohibited claims, competitor mentions.
- Legal review for regulated industries: financial promissory language, health claims.
- Marketer schedules send only after all checkpoints pass in your project management tool.
| Draft type | AI role | Human gate |
|---|---|---|
| Marketing email | First draft copy and variant subjects | CAN-SPAM and brand approval |
| Landing page | Hero text, feature bullets, meta description | SEO and legal on claims |
| Blog post | Outline and section drafts | Editorial fact-check |
| Ad social snippet | Short variants for ads connector | Platform policy review |
CAN-SPAM Compliance for AI Email Drafts
Automated scanners should flag AI drafts missing physical address placeholders, misleading urgency, or unsubscribe suppression before marketers open the draft. CAN-SPAM applies to commercial email in the United States regardless of whether a human or model wrote the body. HubSpot templates should include non-removable compliance modules the AI cannot edit via API.
Attribution and UTM Consistency
AI-generated links must use your canonical UTM naming convention from a locked parameter sheet, not invented campaign values per draft. Fragmented utm_campaign strings break HubSpot attribution reports and Google Analytics comparisons. Inject UTMs programmatically after generation rather than trusting model output.
- Central UTM registry: utm_source, utm_medium, utm_campaign allowed values.
- Post-process every href in AI HTML through a link rewriter that adds or corrects UTMs.
- Align HubSpot campaign object IDs with utm_campaign for closed-loop reporting.
- Reject drafts where utm_content or utm_term fall outside approved patterns.
- Document Q1 2026 campaign codes so AI research assistants do not cite retired naming.
Connecting AI Automation Workflows
AI automation platforms can listen to HubSpot webhooks, enrich contacts, and write only allowlisted properties before enrolling nurtures. Keep automation logic idempotent: the same contact property change should not spawn duplicate AI jobs. Use deduplication keys in your queue.
Compliance Checkpoint Before Publish
Every AI-generated marketing asset passes a compliance checkpoint checklist stored in your project tool before HubSpot status moves from draft to scheduled. Checklist items include CAN-SPAM footer elements, GDPR personalization legality for EU segments, claim substantiation links, and UTM validation. No checkbox, no schedule. Automate checklist creation when the private app creates a draft via API.
Regulated industries should add MLR or legal review steps the AI cannot bypass with API calls. HubSpot user permissions should prevent the integration service account from clicking publish or schedule send. Separation of duties matters as much as prompt engineering.
Brand Voice and Template Locking
Lock HubSpot email template modules for logo, address, and unsubscribe so AI only fills designated rich text regions. Free-form HTML generation bypasses brand CSS and breaks mobile rendering. Provide the model a style guide excerpt in the system prompt, not the entire brand wiki.
Multi-Brand HubSpot Accounts
Business units with separate brand identities need separate private apps or strict business unit filters on every API call. Cross-brand contact merges plus AI personalization create embarrassing send errors. Map hubspot_brand_id metadata on every draft the integration creates.
Rollout and Marketer Training
Pilot on one newsletter and one landing page template before enabling AI across all brand workspaces. Train marketers on editing AI drafts for voice, verifying facts, and running the compliance checklist manually even when scanners pass. Trust but verify UTM injection on every link before publish.
Document three approved AI use cases and three prohibited examples: personalized nurture copy with consent is in scope; rewriting unsubscribe preferences is not. Marketers remember concrete scenarios better than policy PDFs. Pair training with office hours where ops reviews live drafts from the private app integration.
A/B Testing AI Variants
HubSpot supports A/B subject line tests; AI can generate variants but humans must ensure each variant passes CAN-SPAM and brand review before the test arms go live. Do not generate ten variants to speed testing if compliance cannot review all ten. UTM parameters must remain consistent across arms so attribution comparisons stay valid.
Frequently Asked Questions
Can AI enroll contacts in HubSpot workflows automatically?
Yes, with automation scopes, but enrollment should require explicit rules marketing ops authored, not model-improvised segmentation. AI may suggest lists; humans or deterministic filters should confirm enrollment. Sudden bulk enrollment spikes warrant rate limits and alerts.
Which GDPR fields must stay AI read-only?
Lawful basis, consent timestamps, subscription legal basis, and deletion request flags are read-only for AI service accounts in all regions. Extend the list with your DPO's property audit. European Data Protection rules may forbid personalization without explicit consent even when fields are technically writable.
How does HubSpot native AI compare to external tools?
HubSpot Breeze and Content Assistant features operate inside HubSpot's compliance boundary; external tools offer model choice and cross-stack automation. Native tools inherit HubSpot send infrastructure; external drafts still need CAN-SPAM review before scheduling in HubSpot.
Which HubSpot private app scopes do AI tools need?
Request read scopes for contacts and campaigns needed for personalization, write scopes for draft content and approved custom properties only, and webhook subscriptions filtered to relevant object types. Avoid blanket crm.objects.contacts.write that could touch subscription status. Rotate private app tokens when vendors change.
What contact properties can AI write?
AI may write only marketing-approved custom enrichment fields; GDPR lawful basis, opt-out, and subscription properties stay read-only for all AI service accounts. Maintain a quarterly allowlist review with legal. Unexpected property writes should trigger alerts in your SIEM or HubSpot audit log exports.
How do CAN-SPAM rules apply to AI email drafts?
CAN-SPAM requires accurate headers, non-deceptive subject lines, physical address, and working unsubscribe regardless of whether AI or humans drafted the body. Automated scanners plus human review before schedule send are mandatory. Lock compliance modules in HubSpot templates so API edits cannot remove required footer elements.
Does HubSpot override UTMs on send?
HubSpot may append tracking parameters on email links; align your UTM sheet with HubSpot tracking settings to avoid duplicate or conflicting parameters. Test one draft send to sandbox contacts and inspect final URLs in click analytics before campaign launch.
Vendor Due Diligence for Marketing AI
Before connecting a marketing AI vendor to HubSpot private apps, collect SOC 2 reports, data processing agreements, and subprocessors lists; confirm contact data used for personalization is not retained for model training without contract language prohibiting it. Re-review when vendors change default LLM providers. Marketing contact exports are high-value targets for compliance audits.
Scoped Apps, Safe Property Writes, Compliant Drafts, Clean UTMs
HubSpot Marketing AI integrations succeed when private apps use minimal OAuth scopes, contact property writes stay on an approved allowlist away from consent fields, email drafts pass CAN-SPAM checkpoints before send, and UTM parameters come from a canonical registry not model improvisation. Marketing ops owns compliance lists; platform teams owns tokens and webhooks.